Blog
 Threat Research
SSHole: High-Severity OpenSSH Vulnerability Turns Disabled Passwords Into Unauthorized Access
By SAFE Threat Research Team Overview An account with no valid password should never accept password authentication. A newly disclosed OpenSSH vulnerability breaks that fundamental security assumption, potentially…

 Threat Research
CVE-2026-18963 Inside the Keycloak Reset-Credentials Bypass and Pre-Auth Account Takeover
A pre-authentication logic flaw in Keycloak 26.0.0–26.7.1 allows an attacker who knows only a victim’s username to change their password – without credentials, phishing, or any victim interaction.…
 Threat Research
TAILWORM Inside the Tailscale SSH Privilege Boundary
Flaws in Tailscale SSH and Serve can cross local privilege boundaries, expose node-local services to tailnet peers, or exhaust resources. SSH paths require policy-authorized access; Serve paths have…
 Blog
Binance’s $6.3 Billion Security Incident: What Happened, the Suspected DevOps Compromise, and How the Funds Moved
On October 29, 2026, something extraordinary happened in the cryptocurrency industry. Billions of dollars in digital assets began moving out of wallets associated with Binance, the world’s largest…
 Threat Research
CVE-2026-115806: Prime Mover PHP Object Injection Leads to Privilege Escalation
1. Introduction CVE-2026-115806 is a PHP object-injection flaw in Prime Mover – Backup and Migration for WordPress. An unauthenticated visitor can store a base64-encoded serialized object in a…
 Blog
The Top 10 Enterprise TPRM Platforms in 2026
Third parties now show up in almost half of all breaches. Verizon’s 2026 Data Breach Investigations Report puts the share at 48%, up 60% in a single year.…
 CTEM
One Vendor Breach, Five Victims: Why Exposure Management and TPRM Are Now the Same Problem
Here’s the number from this year I can’t stop thinking about: every vendor breach in 2025 hit an average of 5.28 downstream organizations. That’s the highest figure on…
 Threat Research
CVE-2026-111497: Inside Node2Shell and the Brotli Decoder Flaw
A vulnerability first surfaced through Node.js has exposed a much broader attack surface in one of the web ecosystem’s most widely embedded compression components. CVE-2026-111497 is an out-of-bounds…
 Threat Research
CVE-2026-54293 NLTK: URL-Encoded Path Traversal in nltk.data.load()
1. Introduction This article examines a path-traversal flaw in nltk.data.load() in NLTK 3.9.4 and earlier, tracked as CVE-2026-54293 with a CVSS v3.1 score of 7.5 (High) and fixed…
 Threat Research
This Week in CVEs: The Week Defenders Lost the Head Start
This week, the normal vulnerability lifecycle broke down. PHP2Shell set the tone for the week. CVE-2026-109618 and CVE-2026-109619, two critical unauthenticated RCEs in PHP, were already being probed…
 Threat Research
CVE-2026-109618 and CVE-2026-109619 PHP2Shell: Critical PHP Flaws Explained and What Organizations Must Do to Mitigate Risk
1. Introduction This article examines two related memory-safety vulnerabilities in the PHP engine, CVE-2026-109618 and CVE-2026-109619. In our reproduced mod_php chain, multipart HTTP requests combine an out-of-memory trigger…
 News
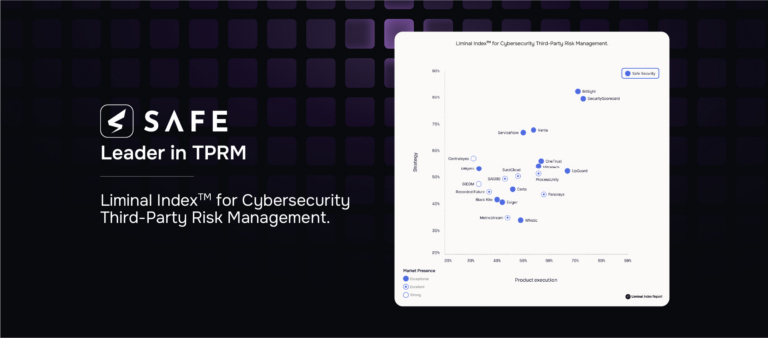
SAFE ranks highest in product execution and strategy in Liminal’s 2026 Cyber TPRM Index
SAFE has been named a Leader in Liminal’s 2026 Cybersecurity Third-Party Risk Management (TPRM) Link Index™ for the second consecutive year. This year, SAFE sits at the far…